Introduction
Cybersecurity threats are entering a new era, and artificial intelligence is playing an increasingly significant role.
The Federal Bureau of Investigation (FBI) has issued a cybersecurity warning about ARTEX, an open-source, AI-powered autonomous penetration-testing framework that malicious actors are using to automate sophisticated cyberattacks against organizations worldwide.
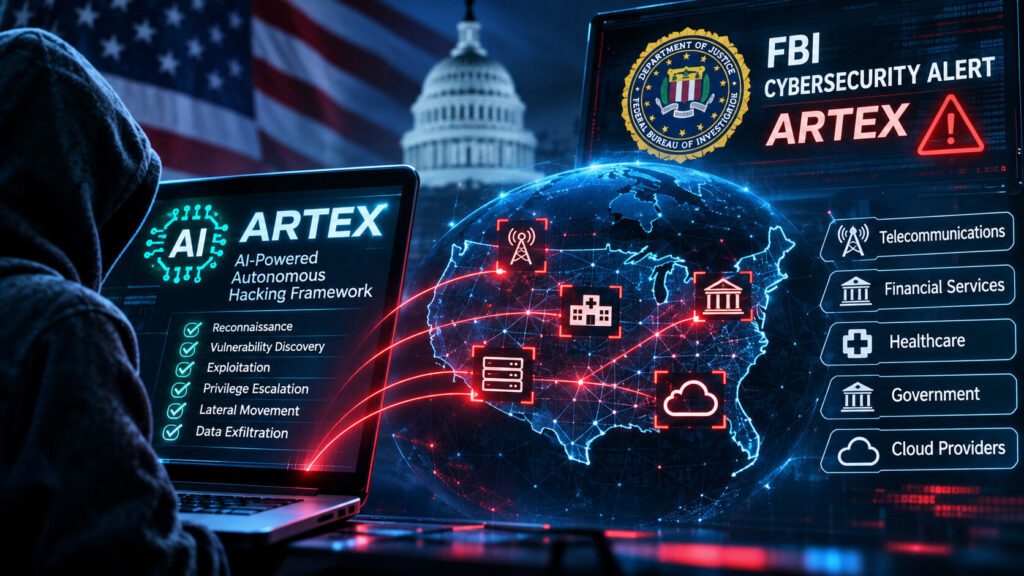
Unlike traditional hacking tools that require operators to manually execute individual commands and analyze results, ARTEX uses artificial intelligence agents to coordinate multiple stages of an intrusion, including reconnaissance, vulnerability discovery, exploitation, privilege escalation, and data exfiltration.
The FBI’s November 13, 2026 advisory highlights how this technology is accelerating cyberattacks, with some intrusions progressing from initial targeting to privileged system access in less than three hours.
The warning comes amid a series of cyber incidents involving telecommunications companies, financial institutions, government organizations, and cloud service providers.
For businesses, the implications are significant: attacks that once required substantial technical expertise and considerable time can now be automated, coordinated, and executed at a much greater scale.
What Is ARTEX?
ARTEX is an open-source autonomous penetration-testing framework powered by large language models (LLMs).
Originally developed for legitimate security testing, the framework allows security professionals to define testing objectives using natural language. Its AI agents then coordinate activities to investigate systems, identify potential weaknesses, and execute authorized security assessments.
However, cybersecurity researchers have documented its use by malicious actors to automate real-world intrusions.
ARTEX does not contain its own proprietary AI model. Instead, it connects to external AI models and uses specialized agents to coordinate security operations.
Depending on the configuration, these integrations can include models from OpenAI, Anthropic, DeepSeek, and other providers.
Its capabilities include:
- Automated reconnaissance: Identifying exposed systems, applications, services, and potential entry points.
- Vulnerability discovery: Searching for software vulnerabilities, insecure configurations, and authentication weaknesses.
- Automated exploitation: Attempting to exploit identified weaknesses.
- Credential discovery: Identifying and abusing exposed credentials and authentication mechanisms.
- Privilege escalation: Attempting to obtain higher levels of access within compromised environments.
- Lateral movement: Exploring opportunities to access additional systems and connected infrastructure.
- Data exfiltration: Collecting and transferring sensitive information from compromised environments.
The primary concern is the level of autonomy. Multiple agents can work simultaneously, adapt to unsuccessful attempts, and pursue alternative attack paths with limited human intervention.
The FBI Warning: Why ARTEX Has Become a Major Cybersecurity Concern
On November 13, 2026, the FBI released an official intelligence advisory titled Threat Overview of ARTEX Autonomous Penetration Testing Framework.
The advisory documents malicious ARTEX activity dating back to at least August 2026.
According to the FBI, threat actors have used the framework to target organizations across several industries, including:
- Financial services and banking.
- Government institutions.
- Telecommunications.
- Healthcare.
- Defense and semiconductor industries.
- Energy and manufacturing.
- Technology companies.
- Legal organizations.
One of the most concerning findings is the speed at which ARTEX-assisted intrusions can progress.
The FBI reports that some attacks have reached privileged access in under three hours.
This significantly reduces the time available for security teams to identify suspicious activity, investigate an incident, and prevent attackers from moving deeper into an organization’s infrastructure.
The FBI also reports that more than 1,600 publicly exposed ARTEX console instances were identified in early November 2026.
Although the original developer removed the public GitHub repository in October following reports of malicious use, independent forks, archived copies, and commercial versions continue to make the framework available.
Major Cybersecurity Incidents Associated With ARTEX
Several documented incidents illustrate the potential consequences of autonomous AI-driven attacks.
1. The ConnectWise Supply-Chain Compromise
One of the most significant incidents involved ConnectWise Cloud Backup, a service used by organizations to protect their Microsoft 365 environments.
Attackers compromised application identities associated with the service and abused previously granted permissions to attempt access to downstream customer environments.
The FBI reported that the attackers attempted authentication against more than 2,250 downstream Microsoft 365 tenants.
This incident highlights the risks associated with third-party integrations, cloud application identities, and excessive permissions.
Even organizations with strong internal security controls can be exposed through a compromised technology provider or trusted integration.
The incident also demonstrates why businesses must continuously review the permissions granted to external applications and service providers.
2. Attacks Against South Korean Financial Institutions
Another campaign involved attacks against South Korean financial institutions.
Researchers documented the use of ARTEX alongside AI coding agents to automate reconnaissance and attack activities.
The campaign resulted in the exfiltration of personal information belonging to approximately 67,000 individuals.
This demonstrates how autonomous offensive frameworks can be used beyond traditional espionage operations and can create serious risks for financial institutions and their customers.
3. The VAPOR PANDA Global Espionage Campaign
Cybersecurity researchers at CrowdStrike documented a campaign attributed to a China-linked threat actor tracked as VAPOR PANDA.
Beginning October 17, 2026, the group used ARTEX alongside AI models to conduct parallel intrusion attempts against more than 200 organizations across 14 countries.
Targets included government ministries, telecommunications providers, pharmaceutical companies, semiconductor organizations, and defense-related entities.
Researchers identified at least nine confirmed organizational compromises.
The campaign is particularly concerning because it demonstrates how AI agents can be coordinated to pursue multiple targets simultaneously rather than focusing on one organization at a time.
It also highlights the growing role of AI in state-linked cyber espionage.
How ARTEX Changes the Cybersecurity Landscape
The emergence of ARTEX reflects a broader transformation in offensive cybersecurity.
Traditional cyberattacks often depended on skilled operators manually identifying vulnerabilities, testing attack paths, and executing individual stages of an intrusion.
AI-driven frameworks can automate substantial portions of this process.
There are three particularly important implications.
1. Lower barriers to entry
Sophisticated penetration-testing capabilities are becoming more accessible. Individuals with limited technical experience may be able to orchestrate complex attack sequences using natural-language instructions and automated agents.
2. Greater attack speed
AI agents can investigate multiple systems, test different approaches, and process findings much faster than traditional manual workflows.
This reduces the time available for security teams to respond.
3. Increased attack scale
Instead of concentrating resources on one target, attackers can coordinate parallel operations against multiple organizations, potentially increasing the number of successful compromises.
The challenge is no longer simply detecting a malicious file or blocking a suspicious IP address. Organizations must identify abnormal behavior across their applications, identities, networks, and cloud environments.
Who Is Most at Risk?
Although ARTEX has been associated with attacks against large enterprises and government organizations, smaller businesses should not assume they are safe.
In many cases, attackers do not need to target an organization directly. They can exploit weaknesses in connected systems, service providers, or third-party applications.
Organizations with the following characteristics should pay particular attention:
- Internet-facing applications with outdated software.
- Weak administrator authentication.
- Exposed remote access and management interfaces.
- Poorly configured cloud environments.
- Excessive permissions granted to third-party applications.
- Unsecured APIs and employee portals.
- Legacy systems that are no longer actively maintained.
- Inadequate monitoring and incident response capabilities.
Small and medium-sized businesses are particularly vulnerable when they rely on limited IT resources and lack continuous security monitoring.
How Businesses Can Protect Themselves
The FBI recommends strengthening access controls, securing exposed applications, monitoring suspicious activity, and reviewing connected infrastructure.
Organizations should consider the following measures.
1. Secure Internet-Facing Applications
Maintain an accurate inventory of publicly accessible websites, applications, APIs, subdomains, and remote access services.
Remove unnecessary services and ensure that exposed applications are regularly updated.
2. Strengthen Authentication
Implement multi-factor authentication (MFA) across administrative accounts, cloud services, hosting platforms, and business applications.
Review existing accounts and immediately disable unused or compromised credentials.
3. Review Third-Party Integrations
Audit connected applications, service accounts, API keys, webhooks, and external integrations.
Remove unnecessary permissions and follow the principle of least privilege.
A trusted application should never automatically receive unrestricted access to sensitive business data.
4. Monitor Cloud Environments
Review Microsoft 365, Google Workspace, AWS, Azure, and other cloud environments for suspicious authentication attempts, unexpected permission changes, unusual application activity, and unauthorized access.
Pay particular attention to service principals, application identities, and automated authentication processes.
5. Implement Continuous Security Monitoring
Traditional security measures are not always sufficient to identify coordinated automated attacks.
Businesses should implement monitoring capable of detecting unusual request patterns, repeated authentication failures, suspicious administrative activity, unexpected file modifications, and abnormal outbound data transfers.
6. Maintain Isolated Backups
Maintain regular, tested backups that are protected from unauthorized modification or deletion.
Backups should be isolated from production systems wherever possible to reduce the impact of ransomware and destructive attacks.
7. Conduct Regular Security Assessments
Perform recurring vulnerability assessments and authorized penetration tests.
Security assessments should cover more than the primary website. They should include APIs, cloud infrastructure, employee portals, staging environments, third-party services, and connected applications.
The Role of AI in the Future of Cybersecurity
ARTEX is an example of a broader shift in how artificial intelligence is changing cybersecurity.
The same technologies that help organizations automate business operations, analyze data, and improve productivity can also be used to automate malicious activities.
However, AI is not inherently malicious. Autonomous security frameworks can also help defenders identify weaknesses, validate security controls, and improve incident response.
The difference is authorization, operational safeguards, and how the technology is deployed.
Security teams must increasingly adopt AI-assisted defensive capabilities to keep pace with automated attacks.
This includes behavioral threat detection, automated vulnerability management, identity monitoring, endpoint detection and response (EDR), and security information and event management (SIEM).
The objective is to reduce the time between detecting suspicious activity and containing a potential compromise.
Conclusion: Cybersecurity Must Evolve Alongside AI
The ARTEX incidents represent an important warning for organizations worldwide.
Cyberattacks are becoming increasingly automated, coordinated, and accessible to a wider range of threat actors.
The FBI’s November 2026 advisory demonstrates that AI-powered frameworks can accelerate intrusions and expose weaknesses across interconnected business environments.
Organizations can no longer rely exclusively on traditional firewalls, antivirus software, or occasional security audits.
They need a comprehensive security strategy that combines strong access controls, continuous monitoring, regular vulnerability assessments, secure cloud configurations, and effective incident response procedures.
As AI continues to transform the cybersecurity landscape, businesses that invest in proactive security and continuous risk management will be better positioned to defend their infrastructure, protect customer information, and maintain operational continuity.
The question is no longer whether attackers will use AI to improve their capabilities. It is whether organizations are prepared to defend themselves against attacks operating at the same speed.
References and Further Reading
- FBI: Threat Overview of ARTEX Autonomous Penetration Testing Framework – November 13, 2026
- CrowdStrike: VAPOR PANDA Uses AI-Driven ARTEX to Grow Global Espionage Campaign
- CERT-EU: From Penetration Testing to Cyber Threat: Beware of ARTEX
- Check Point Research: Hacking on Autopilot: Inside ARTEX Cybercrime Campaigns
- The Record: FBI Flash Alert Says ARTEX Is Automating Cyberattacks at Machine Speed
This article is based on publicly available cybersecurity research and government advisories published as of November 18, 2026.
Share this article
Find your vulnerabilities before attackers do